 dependabot[bot]
e95045905b
Bumps [better-auth](https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth) from 1.6.23 to 1.6.25. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/better-auth/better-auth/releases">better-auth's releases</a>.</em></p> <blockquote> <h2>v1.6.25</h2> <h2><code>better-auth</code></h2> <h3>Bug Fixes</h3> <ul> <li>Fixed Apple OAuth not sending the PKCE code challenge during authorization, causing token exchange failures (<a href="https://redirect.github.com/better-auth/better-auth/pull/10294">#10294</a>)</li> <li>Fixed Google One Tap creating new users when sign-up was disabled on the Google provider (<a href="https://redirect.github.com/better-auth/better-auth/pull/10479">#10479</a>)</li> <li>Fixed <code>$fetch</code> and <code>$store</code> not being exposed on the Solid client (<a href="https://redirect.github.com/better-auth/better-auth/pull/10444">#10444</a>)</li> <li>Fixed internal adapter queries being routed to the wrong table when a built-in table's <code>modelName</code> was set to another table's schema key (e.g. <code>user.modelName = "account"</code>).</li> </ul> <p>For detailed changes, see <a href="https://github.com/better-auth/better-auth/blob/07a646ea190167370fbbb60a0fa2c3be3bec5522/packages/better-auth/CHANGELOG.md"><code>CHANGELOG</code></a></p> <h2>Contributors</h2> <p>Thanks to everyone who contributed to this release:</p> <p><a href="https://github.com/birkskyum"><code>@birkskyum</code></a>, <a href="https://github.com/jsj"><code>@jsj</code></a>, <a href="https://github.com/krish-vachhani"><code>@krish-vachhani</code></a></p> <p><strong>Full changelog:</strong> <a href="https://github.com/better-auth/better-auth/compare/v1.6.24...v1.6.25"><code>v1.6.24...v1.6.25</code></a></p> <h2>v1.6.24</h2> <h2><code>better-auth</code></h2> <h3>Features</h3> <ul> <li>Added request context (<code>ctx</code>) as a third argument to <code>verifyIdToken</code>, enabling custom ID token verifiers to read request headers (<a href="https://redirect.github.com/better-auth/better-auth/pull/10376">#10376</a>)</li> <li>Added <code>beforeStoreCookie</code> option to the last-login-method plugin for GDPR compliance (<a href="https://redirect.github.com/better-auth/better-auth/pull/5753">#5753</a>)</li> </ul> <h3>Bug Fixes</h3> <ul> <li>Replaced flaky MongoDB where-coercion integration test with a direct unit test for more reliable test runs (<a href="https://redirect.github.com/better-auth/better-auth/pull/10369">#10369</a>)</li> <li>Fixed the <code>get-session</code> endpoint to include <code>no-store</code> cache control headers, preventing stale session data from being served (<a href="https://redirect.github.com/better-auth/better-auth/pull/10222">#10222</a>)</li> <li>Fixed SQLite migration diffs to recognize <code>BIGINT</code> as a valid number type, preventing spurious pending changes on rate limiter columns (<a href="https://redirect.github.com/better-auth/better-auth/pull/10316">#10316</a>)</li> <li>Fixed auth requests failing when request cloning throws an error inside verification callbacks (<a href="https://redirect.github.com/better-auth/better-auth/pull/10336">#10336</a>)</li> <li>Fixed <code>useSession({ throw: true })</code> incorrectly excluding <code>null</code> from its <code>data</code> type (<a href="https://redirect.github.com/better-auth/better-auth/pull/9787">#9787</a>)</li> <li>Fixed auth query revalidation and signal listeners not being restored after a client component remounts (<a href="https://redirect.github.com/better-auth/better-auth/pull/10379">#10379</a>)</li> <li>Fixed the <code>CookieAttributes</code> index signature type to be more precise (<a href="https://redirect.github.com/better-auth/better-auth/pull/10442">#10442</a>)</li> <li>Fixed silent misrouting of adapter queries when <code>user.modelName</code> was set to a value that collides with another schema key (<a href="https://redirect.github.com/better-auth/better-auth/pull/10235">#10235</a>)</li> <li>Fixed Kysely migration generation producing duplicate indexes for fields marked both <code>unique</code> and <code>index</code> (<a href="https://redirect.github.com/better-auth/better-auth/pull/10357">#10357</a>)</li> <li>Fixed magic-link and email-OTP send endpoints to validate the <code>Origin</code> header on cookieless requests, preventing cross-origin abuse (<a href="https://redirect.github.com/better-auth/better-auth/pull/10368">#10368</a>)</li> <li>Fixed remote MCP auth 401 challenge headers being hidden from browser clients due to missing CORS exposure (<a href="https://redirect.github.com/better-auth/better-auth/pull/10290">#10290</a>)</li> <li>Fixed OpenAPI schema to include plugin user fields (such as <code>username</code> and <code>displayUsername</code>) in <code>/sign-up/email</code> and <code>/update-user</code> request bodies (<a href="https://redirect.github.com/better-auth/better-auth/pull/10453">#10453</a>)</li> <li>Fixed <code>organization.listMembers</code> failing with "User not found for member" for organizations with more than ~100 members (<a href="https://redirect.github.com/better-auth/better-auth/pull/10342">#10342</a>)</li> <li>Fixed organization invitations to use database-generated IDs when <code>advanced.database.generateId</code> is configured, matching the behavior of other models (<a href="https://redirect.github.com/better-auth/better-auth/pull/10040">#10040</a>)</li> <li>Fixed <code>getDefaultModelName</code> to prefer exact schema key matches over <code>modelName</code> aliases, preventing adapter queries from being misrouted when a built-in table's name collides with another schema key</li> </ul> <p>For detailed changes, see <a href="https://github.com/better-auth/better-auth/blob/9a661c7b7abceaa81123b2c56757ee24f3ad2ed6/packages/better-auth/CHANGELOG.md"><code>CHANGELOG</code></a></p> <h2><code>auth</code></h2> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/better-auth/better-auth/blob/main/packages/better-auth/CHANGELOG.md">better-auth's changelog</a>.</em></p> <blockquote> <h2>1.6.25</h2> <h3>Patch Changes</h3> <ul> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10479">#10479</a> <a href="https://github.com/better-auth/better-auth/commit/5124c3487903e96223bb3f54347724bb0204bb95"><code>5124c34</code></a> Thanks <a href="https://github.com/krish-vachhani"><code>@krish-vachhani</code></a>! - Prevent Google One Tap from creating new users when sign-up is disabled for the Google provider.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10444">#10444</a> <a href="https://github.com/better-auth/better-auth/commit/743935991f9991e8243d6c3d14773b9cfca462e8"><code>7439359</code></a> Thanks <a href="https://github.com/birkskyum"><code>@birkskyum</code></a>! - Expose the real <code>$fetch</code> instance and <code>$store</code> atoms from the Solid client instead of resolving them as dynamic API routes.</p> </li> <li> <p>Updated dependencies [<a href="https://github.com/better-auth/better-auth/commit/0ffd1fb28d44a8266d62791cd4c97e263444d03b"><code>0ffd1fb</code></a>]:</p> <ul> <li><code>@better-auth/core</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/drizzle-adapter</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/kysely-adapter</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/memory-adapter</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/mongo-adapter</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/prisma-adapter</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> <li><code>@better-auth/telemetry</code><a href="https://github.com/1"><code>@1</code></a>.6.25</li> </ul> </li> </ul> <h2>1.6.24</h2> <h3>Patch Changes</h3> <ul> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10235">#10235</a> <a href="https://github.com/better-auth/better-auth/commit/03dc5a046f536994950800ea557b8e2e2e0cdfdd"><code>03dc5a0</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - Fixes silent foreign-key and adapter-join misrouting when a user remaps a built-in model name to a string that collides with another schema key</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10357">#10357</a> <a href="https://github.com/better-auth/better-auth/commit/750894037639c4158472cc1d4994b0e07bf1f59a"><code>7508940</code></a> Thanks <a href="https://github.com/c-nicol"><code>@c-nicol</code></a>! - Fixes Kysely migration generation for new-table fields that are both unique: true and index: true.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10342">#10342</a> <a href="https://github.com/better-auth/better-auth/commit/bae71988ab79aeb4f19f245ceabac9eca8706a50"><code>bae7198</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - Fix <code>organization.listMembers</code> failing with "User not found for member" for orgs with more than ~100 members by applying the same membership limit to the users query.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10336">#10336</a> <a href="https://github.com/better-auth/better-auth/commit/ef4d27360cec8a0bc11a94e135ea4a3dd32b1969"><code>ef4d273</code></a> Thanks <a href="https://github.com/Tushar-Khandelwal-2004"><code>@Tushar-Khandelwal-2004</code></a>! - Prevent verification callbacks from failing auth requests when cloning the request throws.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10333">#10333</a> <a href="https://github.com/better-auth/better-auth/commit/99dbdd7ea98740d11689394220a718dfb9579276"><code>99dbdd7</code></a> Thanks <a href="https://github.com/c-nicol"><code>@c-nicol</code></a>! - Fixes Drizzle schema generation for fields that are both unique: true and index: true.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10368">#10368</a> <a href="https://github.com/better-auth/better-auth/commit/086ca91f51dd8158aff6cbf54c4f9c7ce220914d"><code>086ca91</code></a> Thanks <a href="https://github.com/gaurav0107"><code>@gaurav0107</code></a>! - Force-validate the request <code>Origin</code> on the magic-link (<code>/sign-in/magic-link</code>) and email-otp (<code>/email-otp/send-verification-otp</code>) send endpoints, including cookieless requests, to match the built-in <code>/sign-in/email</code> and <code>/sign-up/email</code> routes. A cookieless cross-origin POST can no longer trigger a magic-link or verification-OTP email to an arbitrary address. Cookieless requests that carry no <code>Origin</code> (server-to-server) are unaffected.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10290">#10290</a> <a href="https://github.com/better-auth/better-auth/commit/8f2dedd89301da9fb52c1a64df6a9683f9be55fd"><code>8f2dedd</code></a> Thanks <a href="https://github.com/GautamBytes"><code>@GautamBytes</code></a>! - Expose the remote MCP auth client's 401 challenge headers to browser clients using CORS.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10453">#10453</a> <a href="https://github.com/better-auth/better-auth/commit/4e685eef420b5576913b9803b58c7e7ee7342203"><code>4e685ee</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - OpenAPI now includes <code>user.additionalFields</code> and plugin user schema fields (e.g. username plugin <code>username</code> / <code>displayUsername</code>) on <code>/sign-up/email</code> and <code>/update-user</code> request bodies.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10190">#10190</a> <a href="https://github.com/better-auth/better-auth/commit/3bf0e4981e025ba9af684013a27b0102a04f7c56"><code>3bf0e49</code></a> Thanks <a href="https://github.com/gaurav-init"><code>@gaurav-init</code></a>! - Pass the endpoint context as the second argument to <code>beforeDeleteOrganization</code> and <code>afterDeleteOrganization</code> hooks in the organization plugin, matching the signature shown in the docs and the existing <code>databaseHooks</code> pattern. The Stripe plugin's <code>beforeDeleteOrganization</code> wrapper now forwards the context to user-supplied hooks instead of dropping it.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10040">#10040</a> <a href="https://github.com/better-auth/better-auth/commit/f59a0ee7895a024ddd4c5c387344173888e17be4"><code>f59a0ee</code></a> Thanks <a href="https://github.com/shiminshen"><code>@shiminshen</code></a>! - Organization invitations now let the database generate their <code>id</code> when ID generation is delegated to the database (e.g. <code>advanced.database.generateId: "uuid"</code> with a UUID-capable adapter such as Postgres), matching every other model. Previously <code>createInvitation</code> always generated the invitation <code>id</code> in application code, so invitation rows received an app-generated value instead of a database-generated one while organizations, members and teams correctly deferred to the database (<a href="https://redirect.github.com/better-auth/better-auth/issues/10024">better-auth/better-auth#10024</a>). A caller-provided id (e.g. via <code>beforeCreateInvitation</code>) is still honored.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10302">#10302</a> <a href="https://github.com/better-auth/better-auth/commit/0f2cc1b33b77850948dac4d889e5f46bba41e8d5"><code>0f2cc1b</code></a> Thanks <a href="https://github.com/momomuchu"><code>@momomuchu</code></a>! - Prefer exact schema-key matches over <code>modelName</code> aliases in <code>getDefaultModelName</code>, so remapping a built-in table onto another table's schema key (e.g. <code>user.modelName = "account"</code>) does not reroute internal adapter queries to the wrong table.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/9787">#9787</a> <a href="https://github.com/better-auth/better-auth/commit/ae781091186f321b4e4ec9e84f64b6e4d5ea1043"><code>ae78109</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - Fixes an issue where <code>useSession({ throw: true })</code> incorrectly excluded <code>null</code> from its <code>data</code> type.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10222">#10222</a> <a href="https://github.com/better-auth/better-auth/commit/46d2bf02c98902da7b344753372d48cfe0e5ebb3"><code>46d2bf0</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - fix: add no-store cache-control headers to get-session route</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10316">#10316</a> <a href="https://github.com/better-auth/better-auth/commit/29a373eaf1778820061a9380c29831c2de2ce704"><code>29a373e</code></a> Thanks <a href="https://github.com/vinay-oppuri"><code>@vinay-oppuri</code></a>! - Recognize SQLite <code>BIGINT</code> as a valid number type in migration diffs so database-backed rate limiter columns like <code>lastRequest</code> no longer report spurious pending changes on every run.</p> </li> <li> <p><a href="https://redirect.github.com/better-auth/better-auth/pull/10379">#10379</a> <a href="https://github.com/better-auth/better-auth/commit/f6d18fa8f79b9323e10b50f72e2b1a088844e4bb"><code>f6d18fa</code></a> Thanks <a href="https://github.com/ping-maxwell"><code>@ping-maxwell</code></a>! - fix(client): restore auth query revalidation and signal listeners after remount</p> </li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/better-auth/better-auth/commit/07a646ea190167370fbbb60a0fa2c3be3bec5522"><code>07a646e</code></a> chore: release v1.6.25 (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10491">#10491</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/743935991f9991e8243d6c3d14773b9cfca462e8"><code>7439359</code></a> fix(solid): expose $fetch and $store on the solid client (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10444">#10444</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/dac701c94bcd777e7cb124570d644f8b4a7981a5"><code>dac701c</code></a> chore(deps): bump next from 16.2.6 to 16.2.11 (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10493">#10493</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/5124c3487903e96223bb3f54347724bb0204bb95"><code>5124c34</code></a> fix(one-tap): enforce google provider signup restrictions (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10479">#10479</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/9a661c7b7abceaa81123b2c56757ee24f3ad2ed6"><code>9a661c7</code></a> chore: release v1.6.24 (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10323">#10323</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/4e685eef420b5576913b9803b58c7e7ee7342203"><code>4e685ee</code></a> fix(open-api): include plugin user fields on sign-up/update bodies (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10453">#10453</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/d3ce7823324ba64efd423895b1c122d85c6d7663"><code>d3ce782</code></a> fix(cookies): tighten CookieAttributes index signature type (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10441">#10441</a>) (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10442">#10442</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/ae781091186f321b4e4ec9e84f64b6e4d5ea1043"><code>ae78109</code></a> fix(client): preserve null in useSession().data type with throw:true (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/9787">#9787</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/f6d18fa8f79b9323e10b50f72e2b1a088844e4bb"><code>f6d18fa</code></a> fix(client): restore auth query lifecycle after remount (<a href="https://github.com/better-auth/better-auth/tree/HEAD/packages/better-auth/issues/10379">#10379</a>)</li> <li><a href="https://github.com/better-auth/better-auth/commit/086ca91f51dd8158aff6cbf54c4f9c7ce220914d"><code>086ca91</code></a> fix(magic-link, email-otp): force-validate Origin on cookieless send endpoint...</li> <li>Additional commits viewable in <a href="https://github.com/better-auth/better-auth/commits/v1.6.25/packages/better-auth">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>

Quickstart · Docs · GitHub · Discord · Twitter · Website


Paperclip is the app people use to manage AI agents for work.
Open-source orchestration for teams of AI agents.
If OpenClaw is an employee, Paperclip is the company.
Paperclip is a Node.js server and React UI that orchestrates a team of AI agents to run a business. Bring your own agents, assign goals, and track work and costs from one dashboard.
It looks like a task manager. Under the hood: org charts, budgets, governance, goal alignment, and agent coordination.
Manage business goals, not pull requests.
| Step | Example | |
|---|---|---|
| 01 | Define the goal | "Build the #1 AI note-taking app to $1M MRR." |
| 02 | Hire the team | CEO, CTO, engineers, designers, marketers — any bot, any provider. |
| 03 | Approve and run | Review strategy. Set budgets. Hit go. Monitor from the dashboard. |
| Works with |
 OpenClaw |
 Claude Code |
 Codex |
 Cursor |
 Bash |
 HTTP |
If it can receive a heartbeat, it's hired.
Paperclip is right for you if
- ✅ You want to build autonomous AI companies
- ✅ You coordinate many different agents (OpenClaw, Codex, Claude, Cursor) toward a common goal
- ✅ You have 20 simultaneous Claude Code terminals open and lose track of what everyone is doing
- ✅ You want agents running autonomously 24/7, but still want to audit work and chime in when needed
- ✅ You want to monitor costs and enforce budgets
- ✅ You want a process for managing agents that feels like using a task manager
- ✅ You want to manage your autonomous businesses from your phone
The four pillars
Four things have to work for an organization of AI agents to actually produce: the tasks, the org, the training, and the infrastructure. Paperclip is built around exactly those four pillars.
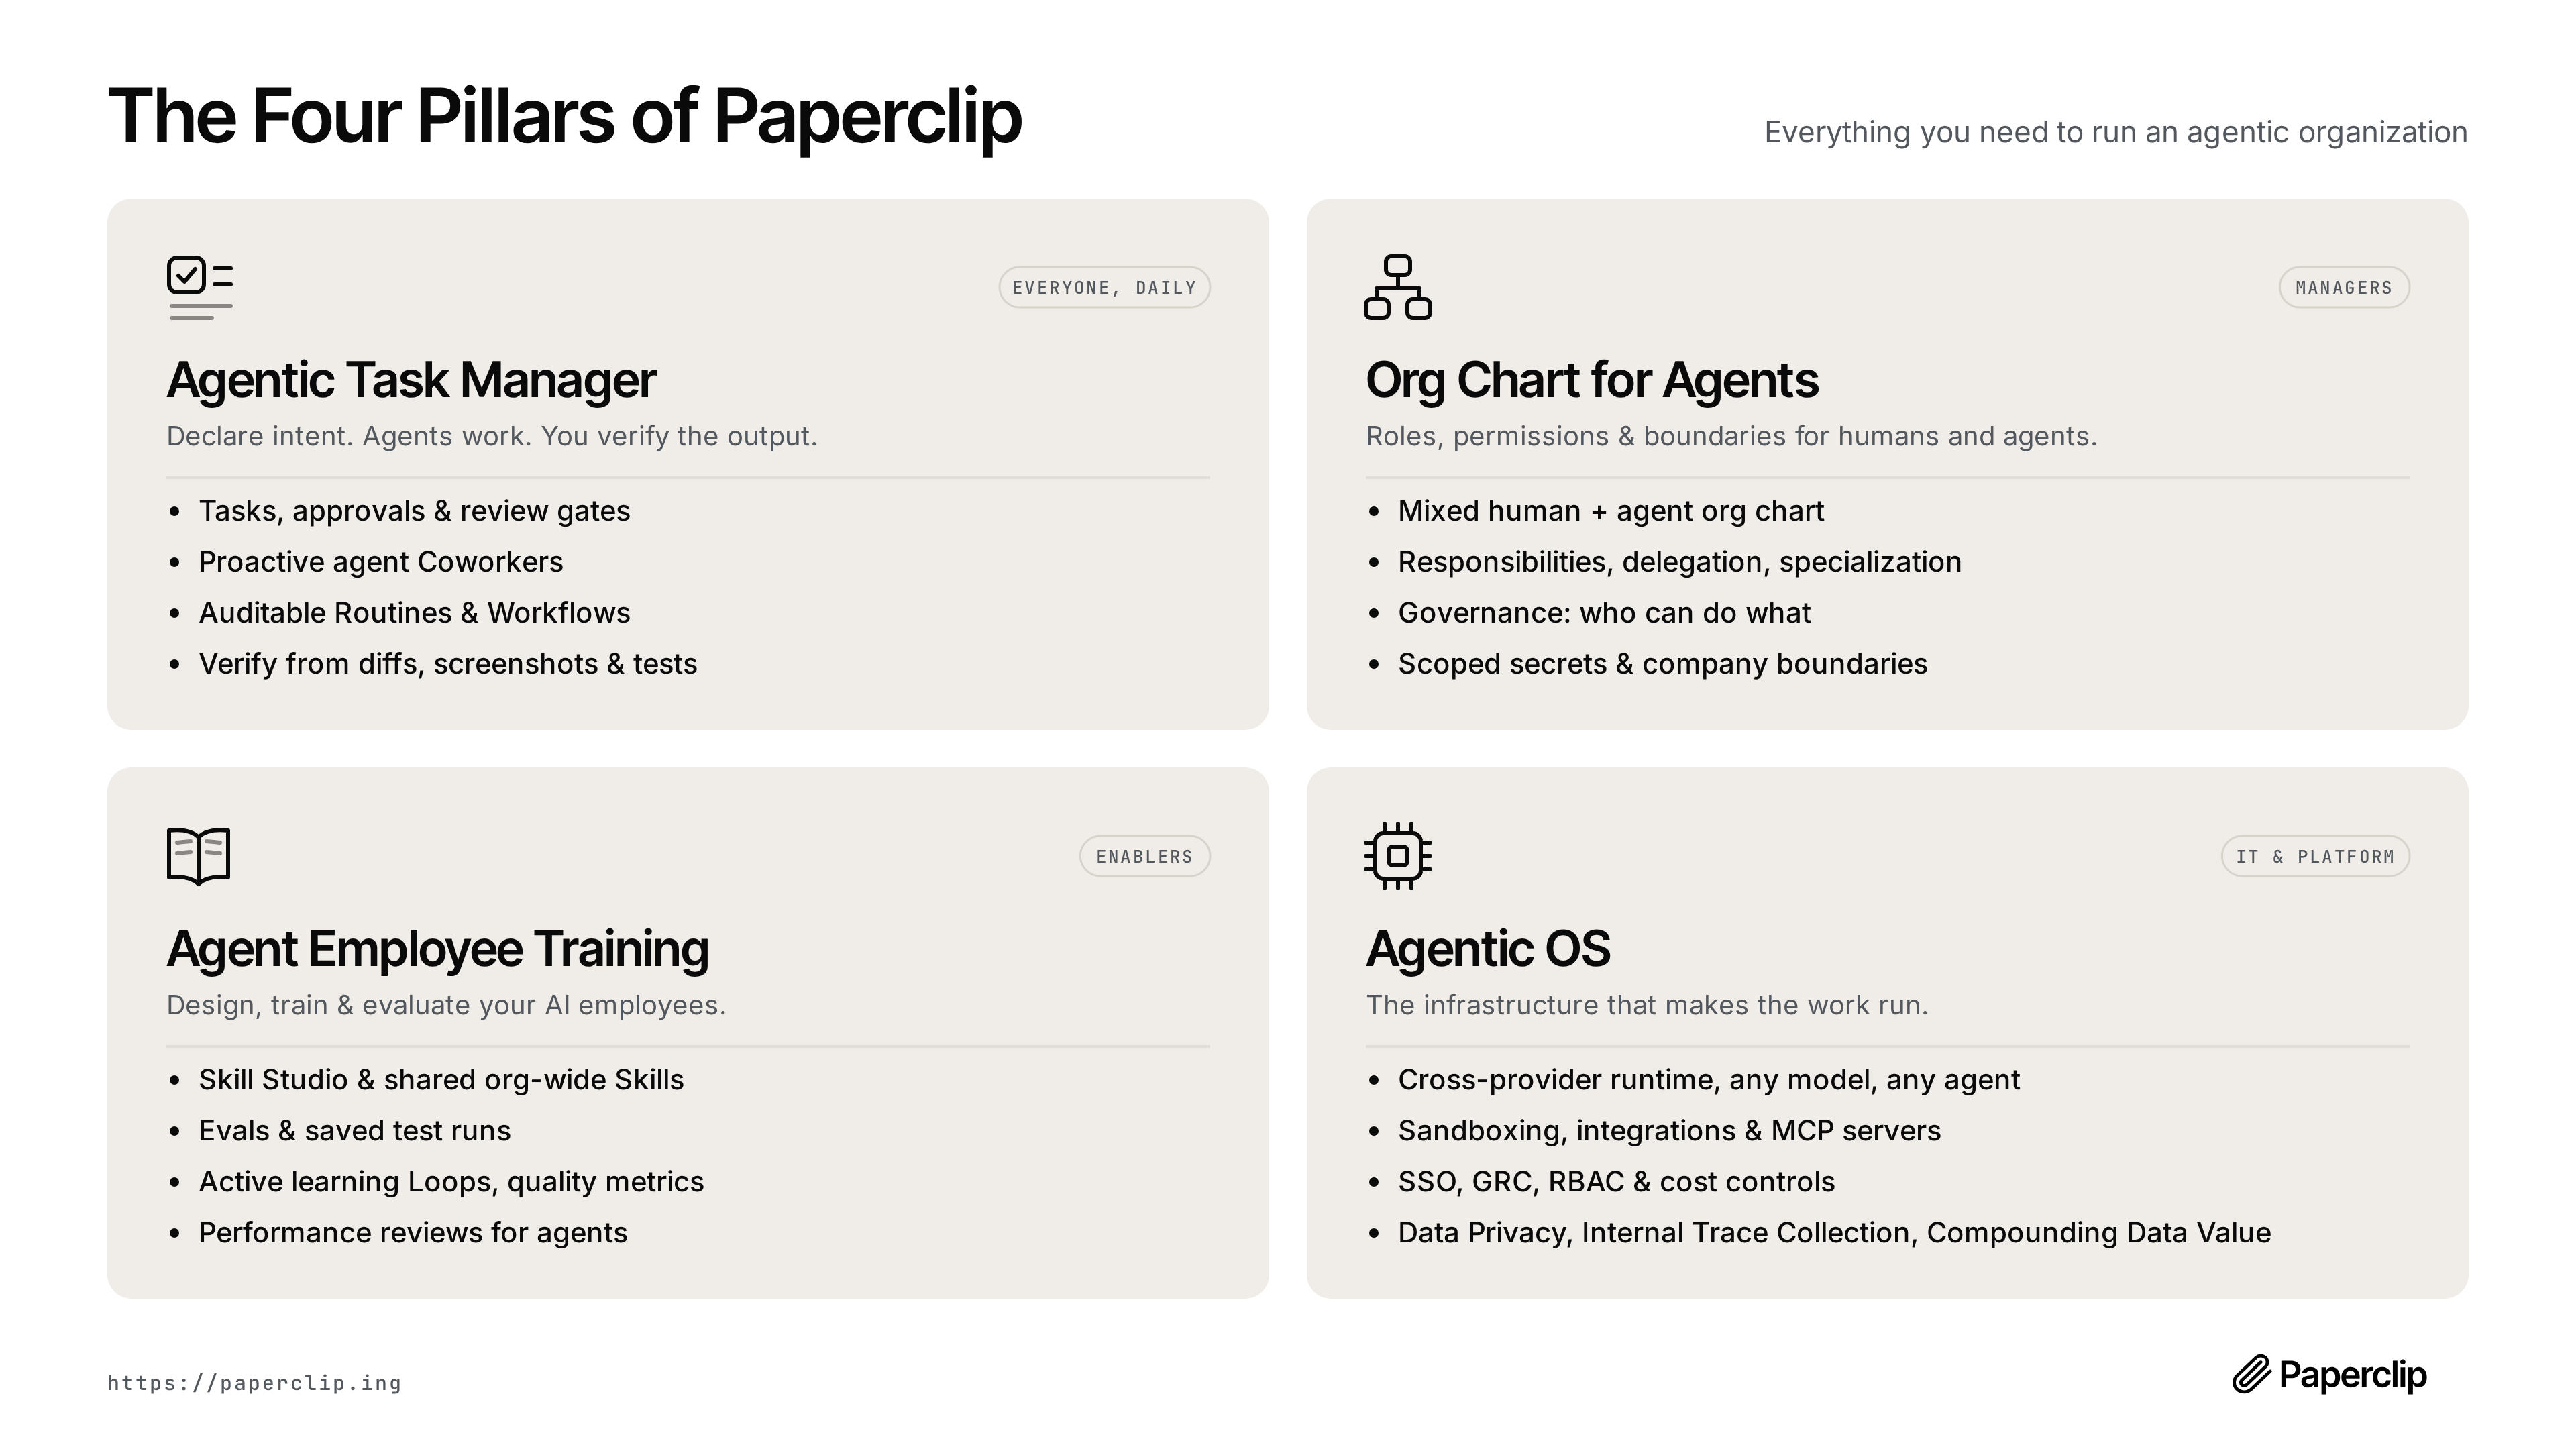
| Pillar | Built for | What it covers |
|---|---|---|
| Agentic Task Manager — Declare intent. Agents work. You verify the output. | Everyone, daily | Tasks, approvals & review gates · proactive agent coworkers · auditable routines & workflows · verify from diffs, screenshots & tests |
| Org Chart for Agents — Roles, permissions & boundaries for humans and agents. | Managers | Mixed human + agent org chart · responsibilities, delegation, specialization · governance: who can do what · scoped secrets & company boundaries |
| Agent Employee Training — Design, train & evaluate your AI employees. | Enablers | Skill Studio & shared org-wide skills · evals & saved test runs · active learning loops & quality metrics · performance reviews for agents |
| Agentic OS — The infrastructure that makes the work run. | IT & platform | Cross-provider runtime: any model, any agent · sandboxing, integrations & MCP servers · SSO, GRC, RBAC & cost controls · data privacy, internal trace collection, compounding data value |
Features
🔌 Bring Your Own AgentAny agent, any runtime, one org chart. If it can receive a heartbeat, it's hired. |
🎯 Goal AlignmentEvery task traces back to the company mission. Agents know what to do and why. |
💓 HeartbeatsAgents wake on a schedule, check work, and act. Delegation flows up and down the org chart. |
💰 Cost ControlMonthly budgets per agent. When they hit the limit, they stop. No runaway costs. |
🏢 Multi-CompanyOne deployment, many companies. Complete data isolation. One control plane for your portfolio. |
🎫 Ticket SystemEvery conversation traced. Every decision explained. Full tool-call tracing and immutable audit log. |
🛡️ GovernanceApprove hires, override strategy, pause or terminate any agent — at any time. |
📊 Org ChartHierarchies, roles, reporting lines. Your agents have a boss, a title, and a job description. |
📱 Mobile ReadyMonitor and manage your autonomous businesses from anywhere. |
Problems Paperclip solves
| Without Paperclip | With Paperclip |
|---|---|
| ❌ You have 20 Claude Code tabs open and can't track which one does what. On reboot you lose everything. | ✅ Tasks are ticket-based, conversations are threaded, sessions persist across reboots. |
| ❌ You manually gather context from several places to remind your bot what you're actually doing. | ✅ Context flows from the task up through the project and company goals — your agent always knows what to do and why. |
| ❌ Folders of agent configs are disorganized and you're re-inventing task management, communication, and coordination between agents. | ✅ Paperclip gives you org charts, ticketing, delegation, and governance out of the box — so you run a company, not a pile of scripts. |
| ❌ Runaway loops waste hundreds of dollars of tokens and max your quota before you even know what happened. | ✅ Cost tracking surfaces token budgets and throttles agents when they're out. Management prioritizes with budgets. |
| ❌ You have recurring jobs (customer support, social, reports) and have to remember to manually kick them off. | ✅ Heartbeats handle regular work on a schedule. Management supervises. |
| ❌ You have an idea, you have to find your repo, fire up Claude Code, keep a tab open, and babysit it. | ✅ Add a task in Paperclip. Your coding agent works on it until it's done. Management reviews their work. |
Why Paperclip is special
Paperclip handles the hard orchestration details correctly.
| Atomic execution. | Task checkout and budget enforcement are atomic, so no double-work and no runaway spend. |
| Persistent agent state. | Agents resume the same task context across heartbeats instead of restarting from scratch. |
| Runtime skill injection. | Agents can learn Paperclip workflows and project context at runtime, without retraining. |
| Governance with rollback. | Approval gates are enforced, config changes are revisioned, and bad changes can be rolled back safely. |
| Goal-aware execution. | Tasks carry full goal ancestry so agents consistently see the "why," not just a title. |
| Portable company templates. | Export/import orgs, agents, and skills with secret scrubbing and collision handling. |
| True multi-company isolation. | Every entity is company-scoped, so one deployment can run many companies with separate data and audit trails. |
What's Under the Hood
Paperclip is a full control plane, not a wrapper. Before you build any of this yourself, know that it already exists:
┌──────────────────────────────────────────────────────────────┐
│                       PAPERCLIP SERVER                       │
│                                                              │
│  ┌───────────┐  ┌───────────┐  ┌───────────┐  ┌───────────┐  │
│  │Identity & │  │  Work &   │  │ Heartbeat │  │Governance │  │
│  │  Access   │  │   Tasks   │  │ Execution │  │& Approvals│  │
│  └───────────┘  └───────────┘  └───────────┘  └───────────┘  │
│                                                              │
│  ┌───────────┐  ┌───────────┐  ┌───────────┐  ┌───────────┐  │
│  │ Org Chart │  │Workspaces │  │  Plugins  │  │  Budget   │  │
│  │ & Agents  │  │ & Runtime │  │           │  │ & Costs   │  │
│  └───────────┘  └───────────┘  └───────────┘  └───────────┘  │
│                                                              │
│  ┌───────────┐  ┌───────────┐  ┌───────────┐  ┌───────────┐  │
│  │ Routines  │  │ Secrets & │  │ Activity  │  │  Company  │  │
│  │& Schedules│  │  Storage  │  │ & Events  │  │Portability│  │
│  └───────────┘  └───────────┘  └───────────┘  └───────────┘  │
└──────────────────────────────────────────────────────────────┘
         ▲              ▲              ▲              ▲
   ┌─────┴─────┐  ┌─────┴─────┐  ┌─────┴─────┐  ┌─────┴─────┐
   │  Claude   │  │   Codex   │  │   CLI     │  │ HTTP/web  │
   │   Code    │  │           │  │  agents   │  │   bots    │
   └───────────┘  └───────────┘  └───────────┘  └───────────┘
The Systems
|
Identity & Access — Two deployment modes (trusted local or authenticated), board users, agent API keys, short-lived run JWTs, company memberships, invite flows, and OpenClaw onboarding. Every mutating request is traced to an actor. |
Org Chart & Agents — Agents have roles, titles, reporting lines, permissions, and budgets. Adapter examples match the diagram: Claude Code, Codex, CLI agents such as Cursor/Gemini/bash, HTTP/webhook bots such as OpenClaw, and external adapter plugins. If it can receive a heartbeat, it's hired. |
|
Work & Task System — Issues carry company/project/goal/parent links, atomic checkout with execution locks, first-class blocker dependencies, comments, documents, attachments, work products, labels, and inbox state. No double-work, no lost context. |
Heartbeat Execution — DB-backed wakeup queue with coalescing, budget checks, workspace resolution, secret injection, skill loading, and adapter invocation. Runs produce structured logs, cost events, session state, and audit trails. Recovery handles orphaned runs automatically. |
|
Workspaces & Runtime — Project workspaces, isolated execution workspaces (git worktrees, operator branches), and runtime services (dev servers, preview URLs). Agents work in the right directory with the right context every time. |
Governance & Approvals — Board approval workflows, execution policies with review/approval stages, decision tracking, budget hard-stops, agent pause/resume/terminate, and full audit logging. Nothing ships without your sign-off. |
|
Budget & Cost Control — Token and cost tracking by company, agent, project, goal, issue, provider, and model. Scoped budget policies with warning thresholds and hard stops. Overspend pauses agents and cancels queued work automatically. |
Routines & Schedules — Recurring tasks with cron, webhook, and API triggers. Concurrency and catch-up policies. Each routine execution creates a tracked issue and wakes the assigned agent — no manual kick-offs needed. |
|
Plugins — Instance-wide plugin system with out-of-process workers, capability-gated host services, job scheduling, tool exposure, and UI contributions. Extend Paperclip without forking it. |
Secrets & Storage — Instance and company secrets, encrypted local storage, provider-backed object storage, attachments, and work products. Sensitive values stay out of prompts unless a scoped run explicitly needs them. |
|
Activity & Events — Mutating actions, heartbeat state changes, cost events, approvals, comments, and work products are recorded as durable activity so operators can audit what happened and why. |
Company Portability — Export and import entire organizations — agents, skills, projects, routines, and issues — with secret scrubbing and collision handling. One deployment, many companies, complete data isolation. |
What Paperclip is not
| Not a chatbot. | Agents have jobs, not chat windows. |
| Not an agent framework. | We don't tell you how to build agents. We tell you how to run a company made of them. |
| Not a workflow builder. | No drag-and-drop pipelines. Paperclip models companies — with org charts, goals, budgets, and governance. |
| Not a prompt manager. | Agents bring their own prompts, models, and runtimes. Paperclip manages the organization they work in. |
| Not a single-agent tool. | This is for teams. If you have one agent, you probably don't need Paperclip. If you have twenty — you definitely do. |
| Not a code review tool. | Paperclip orchestrates work, not pull requests. Bring your own review process. |
Quickstart
Open source. Self-hosted. No Paperclip account required.
npx paperclipai onboard --yes
Troubleshooting: private npm registry
.npmrcIf this fails with an
E404forpaperclipai(or similar) and you use a private npm registry (for example GitHub Packages) via a global~/.npmrc,npxmay be resolvingpaperclipaiagainst that private registry instead of the public npm registry.Diagnostic:
npm config get registryWorkaround (cross-platform; force the public npm registry for this command):
npx --registry https://registry.npmjs.org paperclipai onboard --yes
That quickstart path now defaults to trusted local loopback mode for the fastest first run. To start in authenticated/private mode instead, choose a bind preset explicitly:
npx paperclipai onboard --yes --bind lan
# or:
npx paperclipai onboard --yes --bind tailnet
If you already have Paperclip configured, rerunning onboard keeps the existing config in place. Use paperclipai configure to edit settings.
Or manually:
git clone https://github.com/paperclipai/paperclip.git
cd paperclip
pnpm install
pnpm dev
This starts the API server at http://localhost:3100. An embedded PostgreSQL database is created automatically — no setup required.
Requirements: Node.js 20+, pnpm 9.15+
FAQ
What does a typical setup look like? Locally, a single Node.js process manages an embedded Postgres and local file storage. For production, point it at your own Postgres and deploy however you like. Configure projects, agents, and goals — the agents take care of the rest.
If you're a solo entrepreneur you can use Tailscale to access Paperclip on the go. Then later you can deploy to e.g. Vercel when you need it.
Can I run multiple companies? Yes. A single deployment can run an unlimited number of companies with complete data isolation.
How is Paperclip different from agents like OpenClaw or Claude Code? Paperclip uses those agents. It orchestrates them into a company — with org charts, budgets, goals, governance, and accountability.
Why should I use Paperclip instead of just pointing my OpenClaw to Asana or Trello? Agent orchestration has subtleties in how you coordinate who has work checked out, how to maintain sessions, monitoring costs, establishing governance - Paperclip does this for you.
(Bring-your-own-ticket-system is on the Roadmap)
Do agents run continuously? By default, agents run on scheduled heartbeats and event-based triggers (task assignment, @-mentions). You can also hook in continuous agents like OpenClaw. You bring your agent and Paperclip coordinates.
Development
pnpm dev              # Full dev (API + UI, watch mode)
pnpm dev:once         # Full dev without file watching
pnpm dev:server       # Server only
pnpm build            # Build all
pnpm typecheck        # Type checking
pnpm test             # Cheap default test run (Vitest only)
pnpm test:watch       # Vitest watch mode
pnpm test:e2e         # Playwright browser suite
pnpm db:generate      # Generate DB migration
pnpm db:migrate       # Apply migrations
pnpm test does not run Playwright. Browser suites stay separate and are typically run only when working on those flows or in CI.
See doc/DEVELOPING.md for the full development guide.
Roadmap
- ✅ Plugin system (e.g. add a knowledge base, custom tracing, queues, etc)
- ✅ Get OpenClaw / claw-style agent employees
- ✅ companies.sh - import and export entire organizations
- ✅ Easy AGENTS.md configurations
- ✅ Skills Manager, Skill Studio & Skills Store
- ✅ Scheduled Routines
- ✅ Better Budgeting
- ✅ Agent Reviews and Approvals
- ✅ Multiple Human Users
- ✅ Cloud / Sandbox agents (e2b, Cloudflare, Daytona, Modal, Novita, self-hosted Kubernetes)
- ✅ Artifacts & Work Products
- ✅ Deep Planning (planning mode, revisioned plans, plan approvals)
- ✅ Enforced Outcomes (watchdogs, recovery actions, review gates)
- ✅ MCP Tool Gateway & Apps (governed tool access)
- ✅ Secrets Manager with per-agent access
- ✅ Activity log & action attribution
- ✅ Self-healing runs & automatic recovery
- ✅ Agent evals & feedback
- ⚪ Memory / Knowledge
- ⚪ MAXIMIZER MODE
- ⚪ Work Queues
- ⚪ Self-Organization
- ⚪ Automatic Organizational Learning
- ⚪ CEO Chat
- 🟡 Cloud deployments (multi-tenant isolation & local→cloud sync shipped)
- ⚪ Desktop App
- ⚪ Bring-your-own-ticket-system (Asana / Linear / Jira as on-ramps)
- ⚪ Connected Apps (one-click integrations, e.g. Vercel)
This is the short roadmap preview. See the full roadmap in ROADMAP.md.
Community & Plugins
Find Plugins and more at awesome-paperclip
Observability
Paperclip ships with opt-in OpenTelemetry auto-instrumentation for the server (traces only). It activates when OTEL_EXPORTER_OTLP_ENDPOINT is set and supports grpc, http/protobuf, and http/json via the standard OTEL_EXPORTER_OTLP_PROTOCOL env var. The @opentelemetry/* packages are optional peer dependencies — install them only if you want tracing. See doc/observability.md for install commands and the full env-var reference.
Telemetry
Paperclip collects anonymous usage telemetry to help us understand how the product is used and improve it. No personal information, issue content, prompts, file paths, or secrets are ever collected. Private repository references are hashed with a per-install salt before being sent.
Contributors changing emitted telemetry events should follow the Telemetry Data Contract. For proposed first-party events that are not in the generated contract yet, follow Telemetry Workflow.
Telemetry is enabled by default and can be disabled with any of the following:
| Method | How |
|---|---|
| Environment variable | PAPERCLIP_TELEMETRY_DISABLED=1 |
| Standard convention | DO_NOT_TRACK=1 |
| CI environments | Automatically disabled when CI=true |
| Config file | Set telemetry.enabled: false in your Paperclip config |
Contributing
We welcome contributions. See the contributing guide for details.
Community
- Discord — Join the community
- Twitter / X — Follow updates and announcements
- GitHub Issues — bugs and feature requests
- GitHub Discussions — ideas and RFC
License
MIT © 2026 Paperclip Labs, Inc
Star History
Open source under MIT. Built for people who want to get work done, not babysit agents.